Chrome blocks the page and shows “Your connection is not private.” Under it sits net::err_cert_authority_invalid.
Chrome is not rejecting the address you typed. It rejects the certificate the site handed over, and the body that signed it. Sometimes the fault is on your laptop. Sometimes it is on the server. This guide covers both, plus the Chromebook cases.
What net::err_cert_authority_invalid Means in Chrome
An SSL certificate is a website’s passport. It ties an encryption key to a domain. Chrome checks it during the handshake, before any passwords or card numbers move.
A Certificate Authority issues that passport. Let’s Encrypt, DigiCert, GlobalSign and Sectigo are the names you see most. Your device keeps a small store of their root certificates.
Authorities rarely sign a customer file with a root. An intermediate certificate sits in between. Chrome walks from the site’s file to the intermediate, then to a stored root. Break one link and the check fails.
Error -202 vs. the other certificate codes
Chromium tracks this error as -202. An expired or not-yet-valid file raises NET::ERR_CERT_DATE_INVALID, code -201, instead. A name mismatch shows up as NET::ERR_CERT_COMMON_NAME_INVALID.
Handshake faults form a separate group. A code like err_ssl_version_interference points at the connection itself, not at who signed the certificate.
Why You See net::err_cert_authority_invalid: Device or Server?
Run one quick test. Open Google, your bank and a news site. If all three fail, your device is the problem. If one site fails for every visitor, the server is.
Causes on your device
A wrong clock tops the list. Certificates carry start and end dates, so a device stuck in 2022 reads a 2026 file as invalid.
Antivirus tools with HTTPS scanning come next. Avast Web Shield, Bitdefender and Kaspersky unwrap your traffic and re-sign it with their own certificate. Chrome sees an Avast file claiming to be google.com and stops.
VPNs and inspecting proxies do the same. A plain proxy failure throws err_tunnel_connection_failed, but one that reads HTTPS traffic triggers -202.
Hotel and airport Wi-Fi can also cause it. The login page intercepts HTTPS requests until you sign in. Old versions of Chrome or your OS may lack newer root certificates too.
Causes on the server
The most common one is a missing chain. The owner uploaded your_domain.crt and left out ca_bundle.crt.
A self-signed certificate, made with OpenSSL for testing, fails the same way. So does a file from an authority too new or small to sit in browser trust stores.
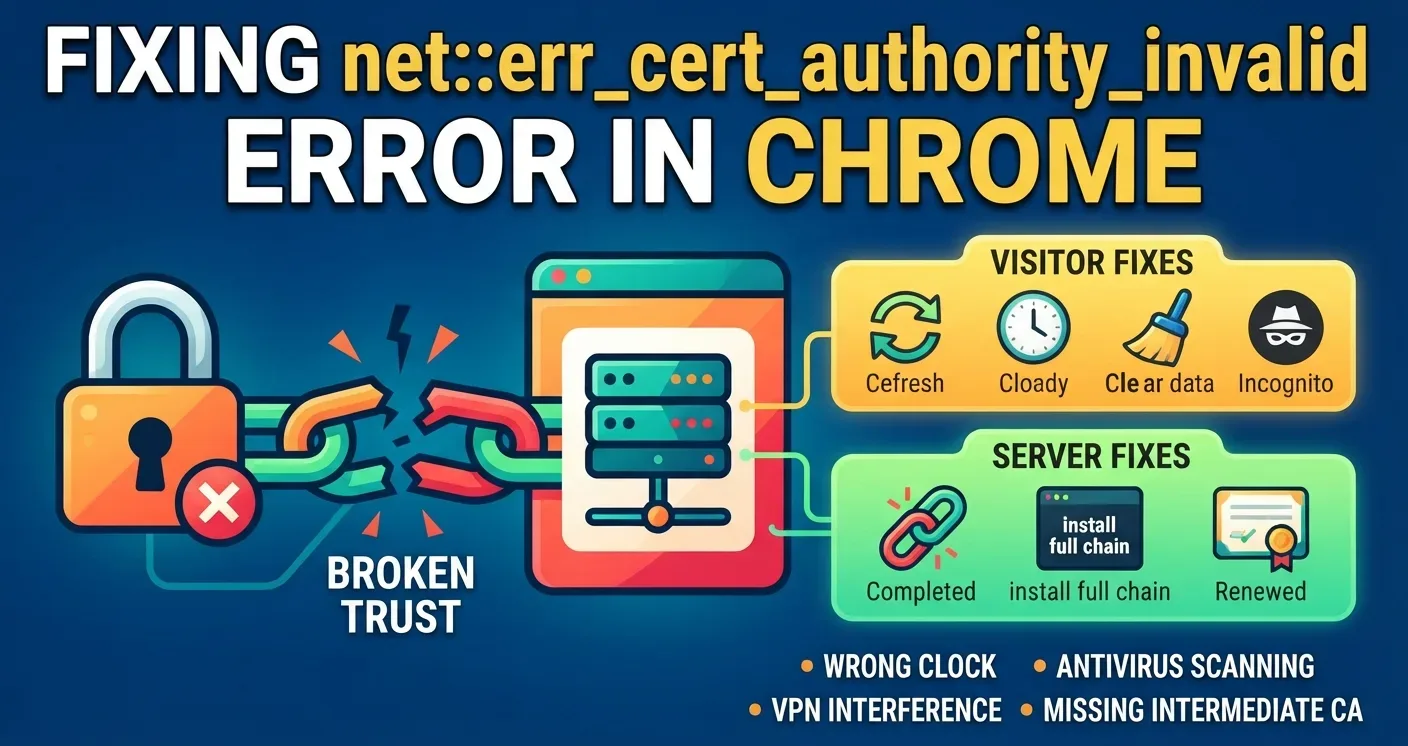
How to Fix net::err_cert_authority_invalid as a Visitor
1. Reload the page
Press Ctrl+R on Windows or Cmd+R on a Mac. A glitch mid-handshake can trip a false alarm. Ctrl+Shift+R fetches every file fresh.
2. Set the clock to automatic
On Windows, open Settings, then Time & language, then Date & time. Switch on “Set time automatically.” On a Mac, go to System Settings, General, Date & Time.
3. Clear saved data
Open chrome://settings/clearBrowserData. Pick “All time,” tick cookies and cached files, then clear. This walkthrough on wiping Chrome’s cache and cookies covers Android and iPhone as well.
Windows keeps its own certificate cache. Clear it from Internet Options, under the Content tab, with “Clear SSL state.”
4. Test in Incognito
Incognito turns most add-ons off. If the page loads there, an extension is at fault. Open chrome://extensions and switch them off one by one until the error returns.
Once you find the culprit, remove it. You can always add a Chrome extension back after the site works again.
5. Pause antivirus HTTPS scanning
Find the HTTPS or SSL scanning option in your security suite and turn it off. Restart Chrome and retry.
If the site now loads, keep the scanner off or whitelist Chrome. These steps for letting Chrome through firewall and antivirus rules do that without leaving your machine open.
6. Update Chrome and change networks
Go to Help, then About Google Chrome, and relaunch if an update waits. Then try mobile data. A page that loads there points at your Wi-Fi, its login screen, or a VPN.
Fixing net::err_cert_authority_invalid on a Chromebook
ChromeOS ships Chrome with the system. Updates come through Settings, then About ChromeOS, not the browser menu.
A Chromebook sets its own time once it goes online, according to Google’s help pages. If the time zone is off, open Settings, System preferences, then Date and time, and pick the right zone.
School and work Chromebooks behave differently. Web filters that inspect HTTPS need a root certificate pushed by the admin. If that push fails, every site shows -202, and only IT can fix it.
On a personal Chromebook, look at the network settings next. A leftover entry in the Chrome proxy configuration can route traffic through a box that re-signs it.
Scanning add-ons belong on the checklist too. Several security extensions for Chromebooks filter page traffic, so disable them before testing.
Server Fixes for net::err_cert_authority_invalid on Your Own Site
Check the chain with SSL Labs
Enter your domain at ssllabs.com/ssltest and wait about a minute. Skip the letter grade. Scroll to Certification Paths. “Chain issues: Incomplete” confirms a missing intermediate.
Install the full certificate bundle
Join the files with your certificate first:
cat your_domain.crt ca_bundle.crt > full_chain.crt
On Nginx, point the server block at the joined file:
ssl_certificate     /etc/ssl/full_chain.crt;
ssl_certificate_key /etc/ssl/private.key;
On Apache 2.4.8 or newer, set SSLCertificateFile to full_chain.crt and SSLCertificateKeyFile to the key. Older builds use SSLCertificateChainFile for ca_bundle.crt. Restart the server and run SSL Labs again.
Replace self-signed files or reissue
Swap a self-signed file for a free Let’s Encrypt one. With shell access, Certbot fetches and installs it. Let’s Encrypt files last 90 days and Certbot renews them before they lapse.
A corrupt install needs a clean start. Run certbot renew –force-renewal, or reissue from your paid authority with a fresh CSR and install the bundle with it.
Don’t wait on this. Google treats HTTPS as a ranking signal, and a blocked site drops in search until the chain is fixed.
Is It Safe to Click “Proceed” Past net::err_cert_authority_invalid?
Not on any page where you log in or pay. Chrome cannot confirm who runs the site, and a copycat can look identical to the real one.
The Advanced link suits one case: a server or router admin page you set up yourself, on your own network.
FAQs
How do I get rid of net::err_cert_authority_invalid?
Reload the page, set your clock to automatic, clear cached data, test in Incognito, and pause antivirus HTTPS scanning. If one site fails for all visitors, its owner must install the full certificate chain.
Why do I get net::err_cert_authority_invalid on every website?
Your device is at fault. A wrong clock, antivirus HTTPS scanning, a VPN, or a school filter re-signing traffic are the usual causes. Fix the clock first, then turn off the scanner.
Why does Reddit show net::err_cert_authority_invalid?
Reddit uses a certificate from a publicly trusted authority, so the fault sits on your side. Check your clock, antivirus HTTPS scanning, VPN, or network filter before loading Reddit again.
Is it safe to bypass net::err_cert_authority_invalid on Reddit?
No. Clicking Proceed on reddit.com can expose your login to whatever is intercepting the connection. Find and fix the device or network cause instead.
Does net::err_cert_authority_invalid mean a site was hacked?
Not always. Most cases trace to a missing intermediate certificate or a self-signed file. Chrome still can’t confirm the site’s identity, so avoid logins and payments until the warning clears.